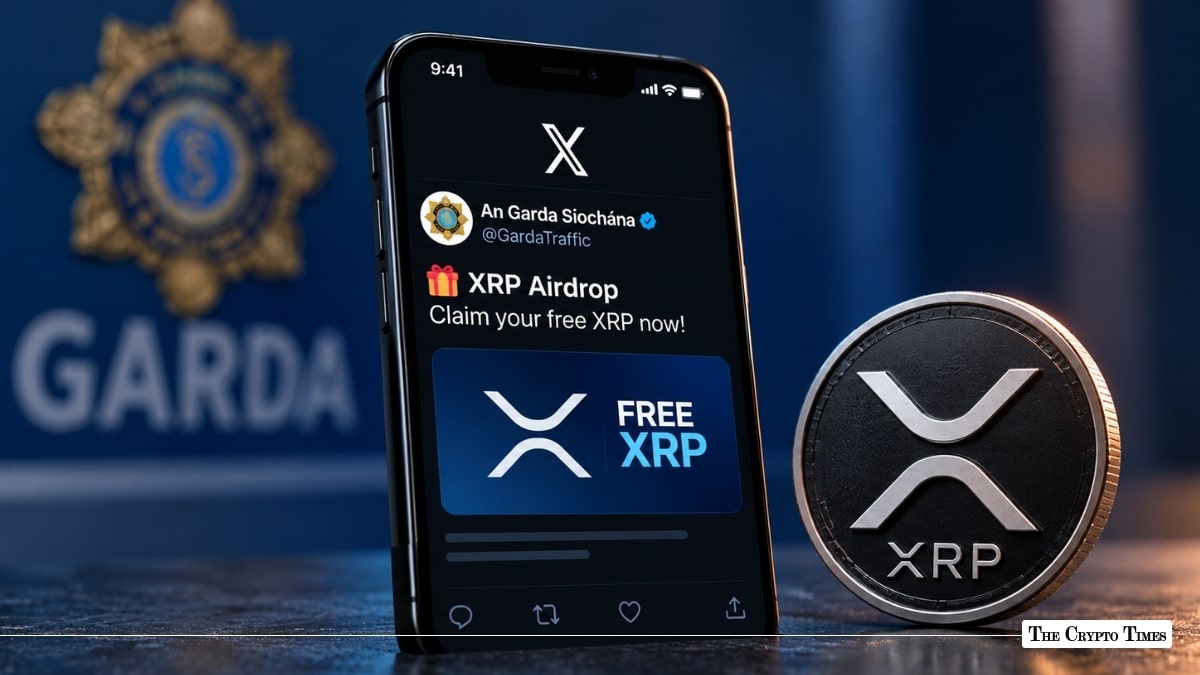
Two official X accounts belonging to An Garda Síochána, Ireland’s national police service, were compromised overnight and used to push a cryptocurrency phishing campaign targeting an XRP allocation. The force has confirmed the breach was limited to the X platform, with no unauthorized access to Garda systems or data.
According to BBC News report, hackers removed Garda branding from @GardaInfo and @GardaTraffic, changed the accounts’ stated location to Amsterdam, and flooded both feeds with posts urging users to claim an XRP “allocation.” X flagged some of the posts with warnings linking them to a suspended profile.
What Happened
On October 14, hackers gained unauthorized access to two official X accounts belonging to An Garda Síochána: @GardaTraffic, which has roughly 600,000 followers, and @GardaInfo, with nearly 300,000 followers. Both accounts began posting promotions for a cryptocurrency shortly after.
The attackers removed the accounts’ official branding and changed their listed location to Amsterdam. They then flooded both feeds with posts urging users to claim an “allocation” of XRP. Some of the posts were flagged by X with warnings linking them to a suspended profile.
@GardaInfo was given new imagery and messaging presenting it as support for Xaman, formerly known as Xumm, a self-custody wallet built for the XRP Ledger, and renamed in a way that framed it as wallet support. Older, legitimate Garda posts remained visible further down the account’s timeline. @GardaTraffic retained part of its original bio describing itself as the force’s traffic and road safety account, even as it carried the crypto posts.
Official Response
An Garda Síochána confirmed the breach on Thursday morning. In a statement, a spokesperson said, “An Garda Síochána can confirm third-party unauthorized access with 2 Official Garda Social Media X accounts @gardainfo and @gardatraffic. This unauthorized access has occurred on the X platform only. An Garda Síochána is satisfied that there is no unauthorized access with any Garda systems and that there is no loss or impact on any Garda data.”
The force told the public not to interact with any content posted on the two accounts, or on accounts purporting to be them. Officials said they are working with X to determine how the unauthorized access occurred and that an internal investigation is underway. Garda accounts on other platforms, including Facebook and Instagram, were not affected.
The Scam Pattern
The posts followed a familiar crypto phishing template: tagging large numbers of users as “eligible” for an XRP allocation or airdrop and directing them toward claim links. Xaman’s own documentation states that the wallet does not run airdrops, has never done so, and never will. Any claim of an Xaman airdrop, rewards program, or free XRP allocation is fake. Connecting a wallet to such sites typically allows attackers to drain funds via malicious signature requests or wallet drainers.
A Recurring Playbook
Hijacking verified, high-follower accounts to push airdrop or token claims has become a recurring tactic, extending beyond crypto-native brands to state agencies and global technology companies. The Crypto Times has previously covered the compromise of Bitcoin hardware wallet maker COLDCARD’s X account, which was used to post a phishing link, and the hijacking of Microsoft’s official X account to promote a Clippy-themed token.
Earlier cases have involved the decentralized exchange Curve Finance, the restaking platform EigenLayer, virtual-world platform Decentraland, and a number of celebrity accounts.
Civil liberties groups in Ireland have described the breach of a state agency’s accounts as “extremely worrying,” noting that social media profiles can sometimes expose additional contact channels even when core systems remain secure.
Protecting XRP Holdings From Fake Airdrop Scams
For XRP Ledger users, the incident underscores a standing rule: Xaman does not run airdrops, rewards programs, or free-allocation claims under any circumstance, according to the wallet’s own documentation. Any message claiming otherwise is fake, regardless of which account posts it.
A verified badge and a large follower count do not confirm an account has not been compromised, since hijacked accounts typically retain both. Users are advised to treat unsolicited “claim your allocation” prompts as a red flag regardless of source and to never connect a wallet or approve a signature request from a link shared in such a post, since doing so can let attackers drain funds through malicious signatures or wallet drainers. Information should be verified through a project’s own website or app rather than through social media links.
Current Status
X has removed the malicious posts. Both Garda accounts remain under scrutiny while the force and the platform investigate how the unauthorized access occurred. The Garda website continues to link to the X profiles in some places, underscoring the importance of verifying official information through garda.ie rather than social media.
Also Read: Three Canadian Armed Forces Members Among 7 Arrested in Toronto Crypto Abduction