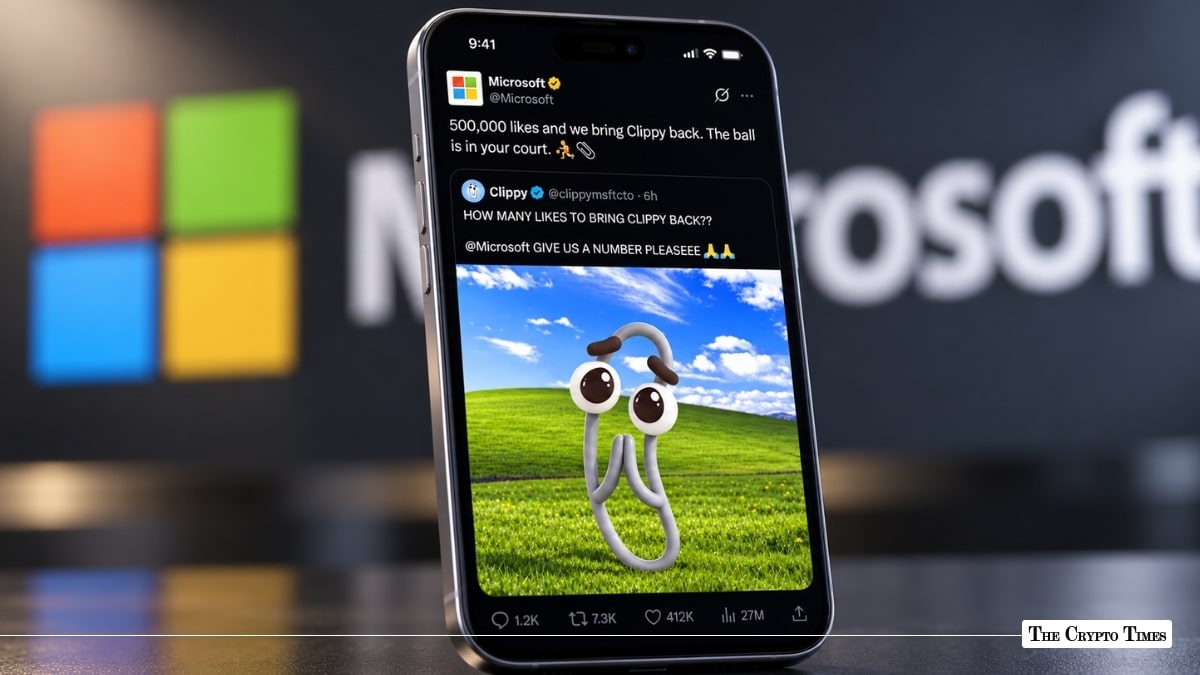
Microsoft’s official X account, which has over 13 million followers, was taken over on October 2 and used to promote a Clippy crypto token.
During the window it followed and reposted @clippymsftcto, an impersonator of the old Office assistant, and its profile picture was swapped for Clippy. The repost was a “500,000 likes and we bring Clippy back” message quoting that account. It has since been removed, so the link may no longer show the text.
International Cyber Digest recorded the sequence, including screenshots of the changed profile and the later apology. That apology disavowed the token and said Microsoft would take legal action. Microsoft then deleted the apology as well.
What Microsoft has confirmed
Spokesperson Brent Colburn told reporters the company had confirmed unauthorized access, including posts that did not come from Microsoft. He said the account has been secured, the unauthorized posts have been removed, and the investigation is continuing.
In the deleted post, Microsoft said it had not authorized, sponsored, or endorsed any cryptocurrency token associated with Clippy, Microsoft, or the MSFT ticker, and that it would pursue unauthorized use of its intellectual property. The real MSFT ticker is Microsoft stock. A token using that name or the Clippy character does not confer shares in Microsoft Corporation.
A second account, @ClippyMSFT, was still promoting a $CLIPPY token after @clippymsftcto was suspended, including a claim of a liquidity pool paired with an MSFT token. That claim is the promoter’s. Microsoft has not verified any pool, any backing by Microsoft shares, or any affiliation.
What is still unknown
Microsoft has not said how the account was accessed. It has not named a suspect. It has not published a restored copy of the apology. X has not posted a public incident note in the material reviewed for this story.
The practical point for anyone who saw the post in the window it was live: it was not a Microsoft product launch. The company has said the opposite, in a statement it then took down, and again through a spokesperson.
No user-loss figure has been published. A hijacked brand account is the tool. Any buy of the token was a trade against an impersonation, not against a Microsoft balance sheet.
Also Read: Bitget Hackers Lose $700K as Script Error Sends USDC, ETH to Wrong Chainflip Channels