Key Highlights
- Blockaid reported that approximately $86,000 was drained from UNCX’s shared vesting pool on Ethereum on October 14.
- ExVul estimated that five ERC-20 tokens worth about $87,700 were affected, with estimated attacker profit of around $84,200 after fees and gas costs.
- ExVul attributed the incident to a suspected accounting flaw involving released and canceled vesting shares in UNCX’s VestingManager contract.
Blockchain security firm Blockaid reported an exploit targeting UNCX’s shared vesting pool on Ethereum, with approximately $86,000 drained by the time of its alert.
In an October 14 X post, Blockaid said the attacker created vesting positions, released a large position, donated tokens back into the pool and canceled a topped-up position. According to Blockaid, the sequence left a small residual position that could be used to withdraw tokens locked by other users.
ExVul estimates $87.7K in affected tokens
In a separate post, ExVul estimated that five ERC-20 tokens worth approximately $87,700 had been drained from UNCX’s Smart Token Vesting contract, using spot prices at the relevant block.
ExVul said the exploit contract held approximately $85,600 in EDGEN, ZC, PEPECOIN, LO0P and PAAL. After accounting for 0.5624 ETH in fees and gas costs, it estimated the attacker’s mark-to-market profit at around $84,200.
These figures are ExVul’s estimates based on prices at a specific point in time. They do not establish the attacker’s confirmed realized proceeds or the final losses.
ExVul identifies suspected vesting accounting flaw
ExVul attributed the incident to how UNCX’s VestingManager contract handled released and canceled vesting shares.
According to its analysis, the contract’s release() function reduced the global _totalTokenShares value but left released shares recorded in the position’s _depositedShares value.
ExVul said the attacker then added tokens to a vesting position and canceled it. During cancellation, the contract allegedly calculated the shares to remove from the position’s full recorded deposit without accounting for shares already released. This caused those shares to be deducted from the global total a second time.
ExVul said a direct token donation amplified the accounting error and distorted the share calculation. The resulting imbalance allegedly allowed the attacker to withdraw tokens backing other users’ vesting positions.
The security account also said this accounting path remained active at the latest block it had checked. However, its post did not establish the contract’s current status.
UNCX restricts new vesting positions
UNCX said on X that it was preventing new vesting positions from entering the contract while reviewing transactions and determining next steps for affected users. The project also announced flat fees of 100 ETH or equivalent across its vesting contracts.
In an update, UNCX said positions in the contracts and other liquidity-provider positions locked through its service were safe. It described the incident as isolated and said it would provide a consolidated update.
These statements reflect UNCX’s assessment. The posts did not include an independent review confirming the status of every position.
Security accounts identify exploit addresses
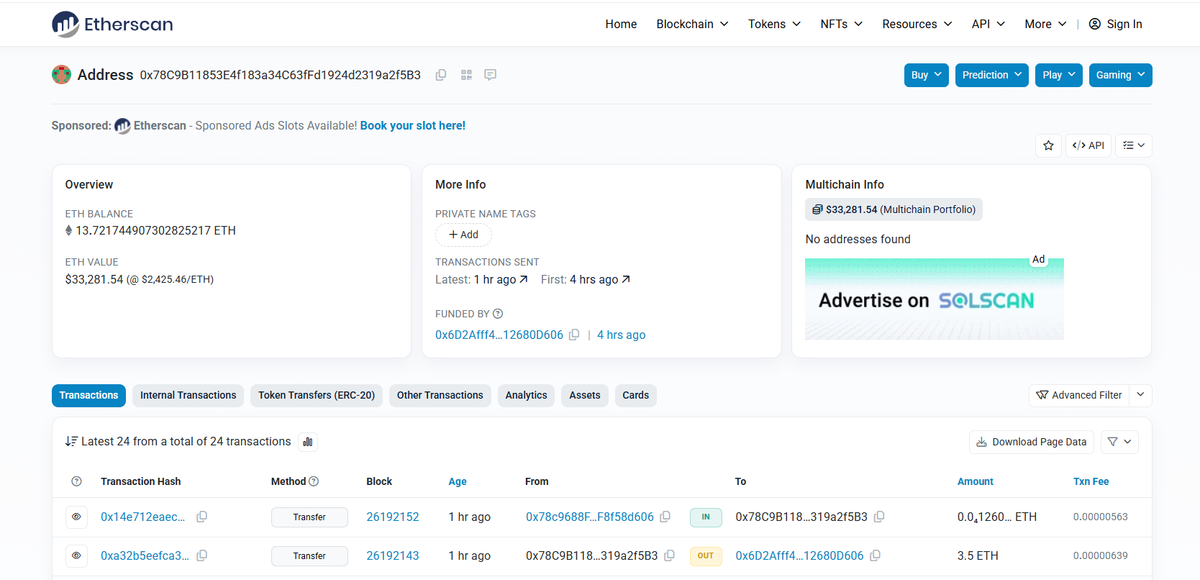
Blockaid identified two Ethereum addresses associated with the incident:
ExVul separately identified the attacker address as 0x78c9b11853e4f183a34c63ffd1924d2319a2f5b3, the exploit contract as 0xf6d072254eb8a9b06e0ba21221b498332c1bc35e, and the UNCX Smart Token Vesting contract as 0xa98f06312b7614523d0f5e725e15fd20fb1b99f5.
ExVul also shared an Ethereum transaction link related to the reported exploit.
Previous Blockaid alerts covered other security risks
Blockaid has also reported unrelated security incidents involving other crypto projects and applications.
On September 16, Blockaid had identified an exploit involving older Flamincome contracts associated with FlamingoFinance. The reported attack used an $18 million USDT flash loan to manipulate VaultYUSDT pricing and extract approximately $345,900.
On September 29, Blockaid warned that malicious text embedded in token names, symbols and descriptions could influence AI agents with wallet access to generate unintended blockchain transactions. These reports involved separate security issues.
X User reports impact on FreeSpeech.FTW
An X user posting as 0xBudderr said FreeSpeech.FTW had been affected and reported approximately $23,000 in token sales while awaiting details about the remaining locked supply.
The account’s posts do not establish the project’s total losses, its full exposure or the outcome of any recovery efforts.
Also Read: US Authorities Shut 241 Websites in Major Crypto Fraud Crackdown