Key Highlights
- NEAR Intents GM Alex Shevchenko said the full $3.8 million taken in the exploit has been returned.
- The recovery came before the October 4 deadline Shevchenko had given the alleged exploiter to return the funds.
- A successful BNB Chain transaction included a message from an address labeled “Near Intents Exploiter 1” saying the funds had been returned.
Alex Shevchenko, general manager of NEAR Intents, said the full $3.8 million taken in the recent exploit has been returned, and the team has stopped its investigation.
In an X post on Friday, Shevchenko announced the recovery, writing that the funds had been “sent back in full” and that the team was “stopping the investigation.” The recovery came before the October 4 deadline Shevchenko had previously set for the alleged exploiter to return the funds.
Earlier return deadline set for October 4
In his earlier recovery request, Shevchenko published three addresses for returning the stolen assets across Bitcoin, BNB/ETH and Solana. He said the alleged exploiter had been identified but did not disclose how the team reached that conclusion.
The latest announcement came before the deadline, with Shevchenko saying the full amount had been returned.
NEAR co-founder says SHIELD helped identify exploiter
NEAR co-founder Illia Polosukhin provided additional details in a separate X post following Shevchenko’s announcement. Polosukhin said the team identified the party responsible less than 24 hours after the exploit and established communication before recovering the funds.
According to Polosukhin, the work involved SHIELD, an AI security layer used by Intents, along with what he described as “aggressive detective work.”
He said the funds were recovered in full at 14:30 UTC and that the investigation had been closed. Polosukhin did not provide technical details about how SHIELD identified the party or explain what specific investigative methods were used.
BNB Chain transaction includes return message
A BNB Chain transaction associated with the return included a message stating that the funds had been sent back. The transaction was marked successful at 4:15:28 PM UTC on October 2 and was sent from an address labeled “Near Intents Exploiter 1” by BscScan.
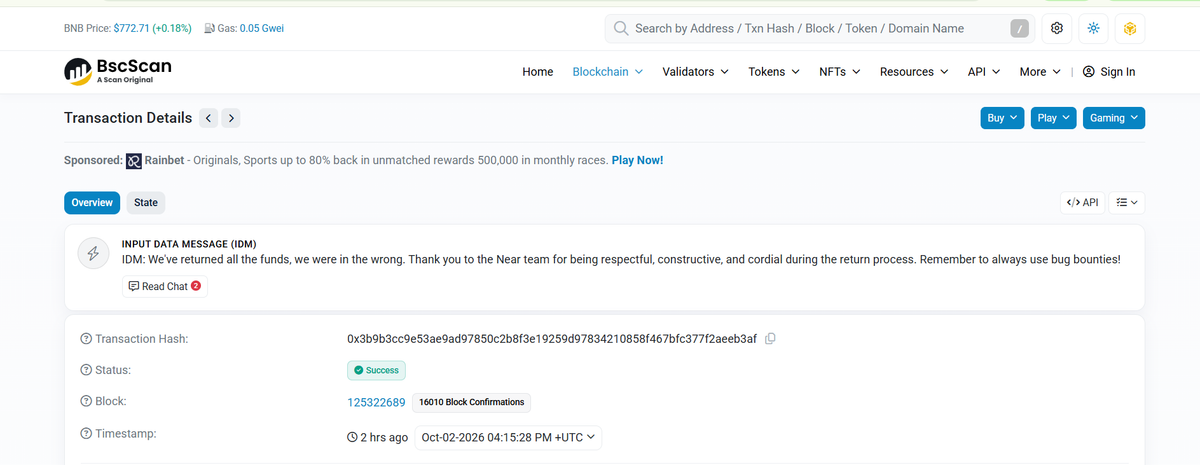
Its input data contained the message:
“We’ve returned all the funds, we were in the wrong. Thank you to the Near team for being respectful, constructive, and cordial during the return process. Remember to always use bug bounties!”
The transaction hash is 0x3b9b3cc9e53ae9ad97850c2b8f3e19259d97834210858f467bfc377f2aeeb3af.
The message does not independently establish who controlled the address, but the transaction is consistent with the reported return of the exploited funds.
Blockchain data shows multiple return routes
Blockchain researcher Kuncoro separately reviewed the addresses published by Shevchenko. According to Kuncoro, the Bitcoin address received 34.59 BTC between 14:31 and 15:05 UTC. Using a quoted Bitcoin price of $85,200, the amount was worth approximately $2.95 million.
Kuncoro also reported that the published BNB/ETH address held 1.04 BNB and 0.30 ETH, while the published Solana address was empty. Based on those figures, Kuncoro estimated that roughly $850,000 had been returned through another route.
Shevchenko responded to the analysis, stating, “You are right. It did indeed.”
The figures were provided by Kuncoro and were not accompanied by a full transaction breakdown from NEAR Intents.
Shevchenko declines to detail tracing
Shevchenko did not provide details about how the team traced the funds or identified the alleged exploiter. When asked how the attacker was found, he replied, “No. We dropped the investigation already.”
Asked who conducted the tracing, Shevchenko said it was the “Internal team.” He did not disclose the methods used by the team or provide additional information about the alleged exploiter.
Shevchenko urges bug-bounty reporting
Shevchenko also urged security researchers to report vulnerabilities through bug-bounty programs rather than exploiting live services. “Please use bug bounties instead of disrupting the services,” he said.
The same message appeared in the BNB Chain transaction data.
Other users subsequently debated the effectiveness and size of bug bounties, but those comments were individual views and did not establish why the exploit occurred.
The $3.8 million was returned before the October 4 deadline set in Shevchenko’s earlier post. NEAR Intents has stopped its investigation, while the team has not disclosed how the alleged exploiter was identified or whether law enforcement was involved.
Also Read: Binance P2P Seller Says SBI Froze ₹4.5 Lakh After a Single $1,000 USDT Sale